# Integration
Grant Fours the necessary permissions to manage your AWS Marketplace on your behalf, no more no less.
---
## Overview
:::info Concurrent Agreements Support
Fours already supports **AWS Marketplace Concurrent Agreements** for SaaS products. This feature allows buyers to make multiple purchases of the same product within a single AWS account, enabling multi-team procurement, mid-term expansions, and repeat purchases without requiring workarounds.
**EventBridge is required** for Concurrent Agreements support. You must enable EventBridge integration to handle multiple active subscriptions. Starting **June 1, 2026**, AWS requires Concurrent Agreements support for all new SaaS products.
:::
1. Visit the [Integration page](https://console.suger.io/settings?tab=integrations) of `suger console`.
>  2. Click the button `CONNECT` and redirect to new browser tab. It will automatically start a `AWS CloudFormation Stack` on your AWS account to create an `IAM role` for Fours to access & manage your `AWS Marketplace` on your behalf.
:::tip
- Contact support@suger.io for the Fours AWS Account ID to fill the stack field `AccountId`.
- Fulfill the field `MdfsS3BucketName` with `suger-mdfs-s3-bucket-{your-aws-account-id}`.
:::
>
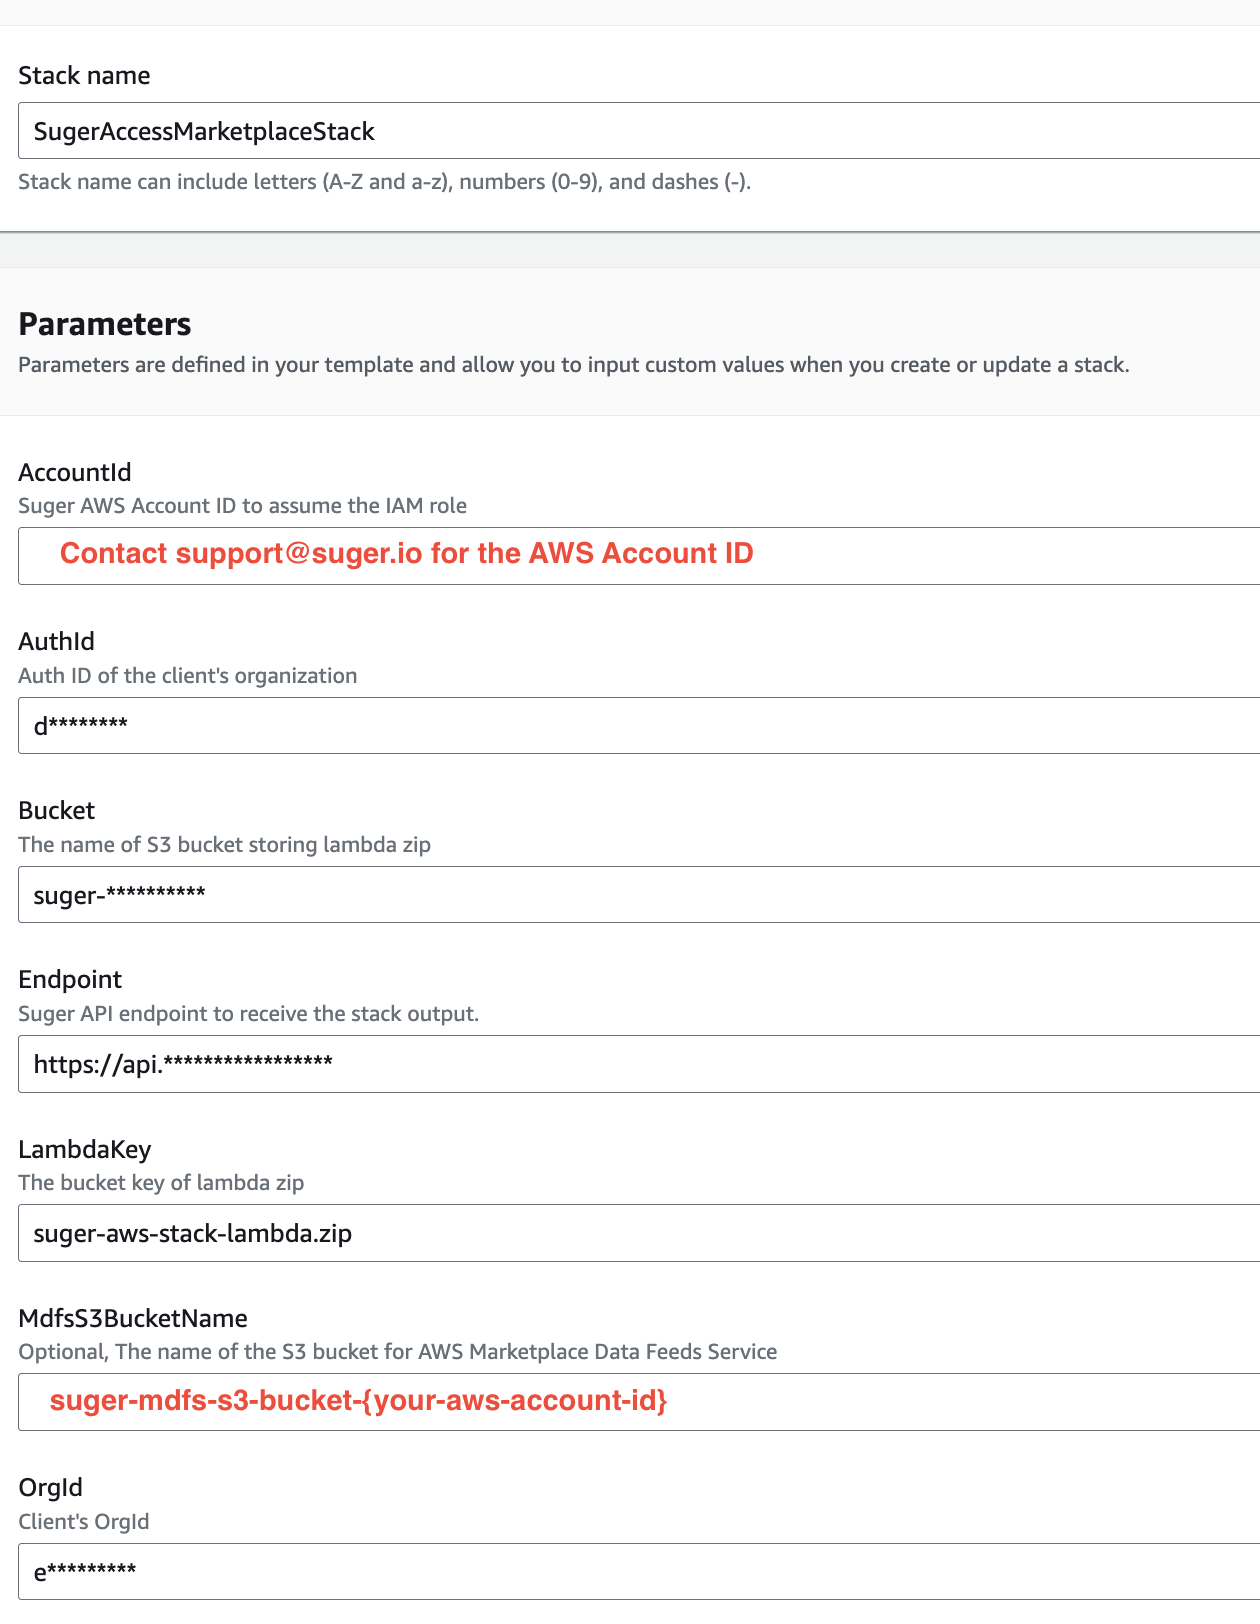 3. Check the box of `I acknowledge that ...` and click button `Create stack`.
4. Wait for a few minutes, the `AWS Marketplace` integration status will be updated as `VERIFIED`.
>
 :::tip
- You may need to click the button `VERIFY` to verify whether the `AWS marketplace` integration works correctly.
:::
:::tip Need to open AWS support cases?
That's a separate **AWS Support** integration — see [AWS Support Cases](/aws-marketplace/support-cases/).
:::
## Edit Integration
You can edit the integration to update the following fields:
- **Enable Entitlement End Soon Notification**: When enabled, specify the number of days (10-60) before an entitlement ends to trigger notifications. Fours will send an initial notification when AWS Marketplace entitlements approach ending, followed by reminders every 5 days. To configure recipients, follow the [email notification configuration guide](https://doc.fours.com/settings/email-notification/#configuration) and add the scope `END_SOON.ENTITLEMENT`.
:::warning The IAM role identity is fixed after creation
The **IAM Role ARN** and **External ID** that identify the role Fours assumes are set once, when the integration is created, and cannot be changed by editing it. Fours restores them from the stored integration on every update and ignores anything sent in their place, so a saved edit never repoints Fours' access at a different role.
If you genuinely need to move the integration to another IAM role — for example after re-deploying the CloudFormation stack into a different AWS account — delete the integration and connect it again. The same rule applies to the AWS Billing, AWS S3, and AWS Partner Central (ACE) integrations. Rotating an access key, or changing the bucket and region on an S3 integration, is still an ordinary edit.
:::
## Delete Integration
The AWS integration can be deleted like all other integrations. Once the deletion icon is clicked & confirmed, the integration info will be deleted immediately & permanently from Fours. No time window or methods to recover.
When more than one AWS account is connected (see [Multiple Integrations](#multiple-integrations)), each account's card is deleted on its own and the other accounts keep working. Deleting the default account makes the oldest remaining account the default. The deleted account's products, offers and entitlements stay in Fours, but Fours can no longer sync them or act on them, because no connected account owns them. Remove that account's `SugerAccessMarketplaceStack` from its own AWS account as described below.
:::warning
- To completely delete the `IAM Role` created for Fours, please visit your [AWS CloudFormation](https://us-west-2.console.aws.amazon.com/cloudformation/home?region=us-west-2), and delete the stack `SugerAccessMarketplaceStack`, which will remove all resources including `IAM Role` created for Fours.
- If you also deployed the standalone EventBridge stack from [Manual EventBridge Setup](#manual-eventbridge-setup), delete that stack as well (in `us-east-1`) to remove the EventBridge Connection, API Destination, Rule, and IAM Role it created.
:::
## Multiple Integrations
You can connect more than one AWS Marketplace seller account to the same Fours organization — for example, when a subsidiary sells from its own AWS account. Each account is its own AWS Marketplace integration with its own card on the [Integrations page](https://console.suger.io/settings?tab=integrations), and each product, offer and entitlement belongs to the account it was listed or sold under.
### Add another AWS account
Connect your first account with the `CONNECT` button, as described in [Overview](#overview). Once an account is connected, you add the next one from its card:
1. On the Integrations page, open your AWS Marketplace card's **⋯** menu and choose **Add another AWS account**.
2. The **Add another AWS Marketplace account** dialog lists the accounts that are **Already connected**, then walks you through three steps:
1. **Sign in to the AWS account you want to add.** Open the AWS console in another browser tab and switch to that seller account. The CloudFormation stack is created in whichever account is signed in, so this step decides which account gets connected.
2. **Give it a name (optional).** Up to 100 characters, shown next to the account ID.
3. **Create the access role.** Click **Open CloudFormation**, fill in the stack fields the same way as for your first account (see step 2 of [Overview](#overview)), and click **Create stack**.
3. Return to the Fours tab once the stack is created. While the dialog is open, Fours checks for the new account automatically for up to 10 minutes and confirms **Connected AWS account** with the account's ID.
If no new account is detected within 10 minutes, the dialog says so. The usual cause is a stack created in an account that is already connected, which changes nothing. Check the stack's status in the AWS CloudFormation console, then click **Retry**.
```d2
shape: sequence_diagram
you: "You"
console: "Fours Console"
aws: "The AWS account\nyou are adding"
suger: "Fours"
you -> aws: "Sign in to that seller account in your browser"
you -> console: "Add another AWS account,\nname it (optional), Open CloudFormation"
console -> aws: "Open the CloudFormation quick-create page"
you -> aws: "Create stack"
aws -> suger: "The stack reports the new access role"
second: "if this is your second account" {
suger -> suger: "Attach your first account's products, offers,\nentitlements and referrals to its account ID,\nand make it the default"
}
console -> suger: "Check for the new account (up to 10 minutes)"
suger -> console: "A new card showing the account's AWS account ID" { style.stroke-dash: 4 }
```
When your second account is connected, every AWS Marketplace card shows the line **AWS account** followed by that account's 12-digit ID, and your first account is marked **Default**. The products, offers, entitlements and referrals you already had stay with that first account. A third or later account is simply added alongside.
When you create a SaaS or Professional Services product while more than one account is connected, choose its account in the **AWS Marketplace Integration** field — see [Create the AWS Marketplace Product](/aws-marketplace/list-product/#step-2-complete-basic-information).
### Choose the default account
The default account is the one Fours uses when a request does not say which account it is for:
- **A buyer arrives from a fulfillment URL with no `partnerId`** — typically a listing created before you connected your second account. If the default account can't read the buyer's registration token, Fours tries your other connected accounts before failing the signup. See [Set up your fulfillment URL](/aws-marketplace/list-product/#set-up-your-fulfillment-url).
- **An API request doesn't name an account** — for example, creating a product without a `partnerID`.
To change the default, open the **⋯** menu on another account's card and choose **Set as default**. The option appears only while more than one account is connected, and only on accounts that are not already the default.
:::tip
Each account's card can be edited, verified or deleted on its own. See [Delete Integration](#delete-integration) for what happens to an account's objects when you delete it.
:::
## AWS IAM Policies
Here is the list of AWS managed policies included in the `Suger Access IAM role`.
| Policy Name | Description |
| -------------------------------------------------------- | :------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| `arn:aws:iam::aws:policy/AWSMarketplaceFullAccess` | This policy grants Fours full access to AWS Marketplace and related services, as well as access to Amazon EC2, AWS CloudFormation, and Amazon EC2 Systems Manager. |
| `arn:aws:iam::aws:policy/AWSMarketplaceSellerFullAccess` | This policy grants Fours to manage your sales (product listings, offers, entitlements & metering) on marketplace. |
| `SugerAccessMarketplacePolicy` | This policy grants Fours necessary-only permissions on `AWS s3` & `AWS SNS` to configure & access your [AWS Marketplace Commerce Analytics Service](https://docs.aws.amazon.com/marketplace/latest/userguide/commerce-analytics-service.html#permissions-for-commerce-analytics) and [AWS Marketplace Data Feeds Service](https://docs.aws.amazon.com/marketplace/latest/userguide/data-feed-service.html). |
:::info
None of these policies grant access to the AWS Support API; the AWS Support integration uses its own IAM role. See [AWS Support Cases](/aws-marketplace/support-cases/).
:::
## Minimum-Permission Deployment (Optional)
The default CloudFormation template requests broad permissions — including `iam:CreateRole`, the `events:*` family, and the AWS-managed `AWSMarketplaceFullAccess` / `AWSMarketplaceSellerFullAccess` policies — so that Fours can automatically provision and maintain the IAM role, EventBridge rule, connection, and API destination required for AWS Marketplace event delivery. With the default template, no further manual work is needed on your side, and new AWS Marketplace capabilities are picked up automatically as we add support.
If your security team prefers a tighter blast radius, **we recommend using a dedicated AWS seller account exclusively for the Fours integration**. A dedicated account is the cleanest way to isolate Fours' access from the rest of your AWS footprint and is what we suggest for most enterprise customers.
If a dedicated seller account is not an option, please contact [Fours Support](mailto:support@suger.io) for a **minimum-permission deployment package**. We can provide a CloudFormation template scoped down to only the actions Fours needs at deploy time.
A minimum-permission role cannot create the EventBridge resources that deliver AWS Marketplace events, so set them up yourself with [Manual EventBridge Setup](#manual-eventbridge-setup) below.
:::warning Trade-offs of the minimum-permission deployment
- AWS Marketplace ships new features regularly, and most of them depend on additional IAM actions. With the default template, Fours picks them up transparently. With the minimum-permission template, support for those new features may temporarily break in your account.
- Each time we add support for a new AWS Marketplace capability that requires extra permissions, you will most likely need to **redeploy an updated minimum-permission CloudFormation stack** before the capability works for you. We will reach out when this is needed, but onboarding new functionality will not be as seamless as with the default template.
:::
### Manual EventBridge Setup
If your Fours Access IAM role does not grant `iam:CreateRole` / `iam:CreatePolicy` / `iam:PutRolePolicy` (for example, because you are running the minimum-permission template, or your security team disallows Fours from creating IAM resources on your behalf), Fours cannot auto-provision the IAM role and EventBridge resources required for [Concurrent Agreements](#overview) and other event-driven capabilities. In that case, deploy the standalone CloudFormation template below — under an AWS principal that *does* have IAM and EventBridge admin permissions — in **the same AWS account and region** as your AWS Marketplace listings. It creates the four resources Fours needs:
- An EventBridge **Connection** with API-key auth (header `x-suger-api-key`): `aws-marketplace-event-connection-manual-${OrgId}`.
- An EventBridge **API Destination** pointing at `${Endpoint}/public/aws/eventbridge/webhook/orgId/${OrgId}`: `aws-marketplace-event-api-destination-manual-${OrgId}`.
- An **IAM Role** that lets EventBridge invoke the API Destination: `event-bridge-invoke-role-manual-${OrgId}`.
- An EventBridge **Rule** matching `aws.marketplacecatalog` and `aws.agreement-marketplace` events and routing them to the API Destination: `aws-marketplace-event-rule-webhook-manual-${OrgId}`.
Every resource name ends in `-manual-${OrgId}`, your Fours organization ID, so the stack never collides with the resources that Fours auto-provisions, and several Fours organizations can each deploy their own stack in the same AWS account. When Fours sets up EventBridge for a new integration itself, it creates a separate rule, connection, API destination and invoke role for each Fours organization, so two Fours organizations that sell from the same AWS account each receive their own events. An integration whose EventBridge setup already exists keeps it as it is.
#### Parameters
| Parameter | Description |
| ---------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `AuthId` | Your organization's **auth ID**, on the [settings page](https://console.suger.io/settings). Sent on every forwarded event as the `x-suger-api-key` header — it is the only value the webhook accepts, so do not generate a separate API key here. |
| `Endpoint` | Fours API base URL: `https://api.suger.cloud`. |
| `OrgId` | Your Fours organization ID, visible on the Fours Console settings page. |
:::tip
- Deploy the stack in **`us-east-1`**. AWS Marketplace SaaS events are emitted from `us-east-1`, and cross-region delivery is not supported by the default rule.
- Treat `AuthId` like any other production secret — set the parameter with `NoEcho` enabled (already the default in the template) and avoid committing it to source control.
:::
#### Template
```yaml
AWSTemplateFormatVersion: '2010-09-09'
Description: Forward AWS Marketplace events to Suger via EventBridge API Destination
Parameters:
AuthId:
Type: String
NoEcho: true
Description: Your Suger organization's auth ID (sent as the x-suger-api-key header)
Endpoint:
Type: String
Description: Suger API base URL, e.g. https://api.suger.cloud
AllowedPattern: ^https?://.+
OrgId:
Type: String
Description: Suger organization ID
AllowedPattern: ^[A-Za-z0-9-]+$
Resources:
SugerMarketplaceConnection:
Type: AWS::Events::Connection
Properties:
Name: !Sub 'aws-marketplace-event-connection-manual-${OrgId}'
Description: API key auth for Suger event ingestion
AuthorizationType: API_KEY
AuthParameters:
ApiKeyAuthParameters:
ApiKeyName: x-suger-api-key
ApiKeyValue: !Ref AuthId
SugerMarketplaceApiDestination:
Type: AWS::Events::ApiDestination
Properties:
Name: !Sub 'aws-marketplace-event-api-destination-manual-${OrgId}'
Description: Suger marketplace event ingestion endpoint
ConnectionArn: !GetAtt SugerMarketplaceConnection.Arn
HttpMethod: POST
InvocationEndpoint: !Sub '${Endpoint}/public/aws/eventbridge/webhook/orgId/${OrgId}'
# Trust policy uses constructed rule ARN (not !GetAtt) to break the cycle
# Rule.Targets -> InvokeRole -> Rule.
SugerEventBridgeInvokeRole:
Type: AWS::IAM::Role
Properties:
RoleName: !Sub 'event-bridge-invoke-role-manual-${OrgId}'
AssumeRolePolicyDocument:
Version: '2012-10-17'
Statement:
- Effect: Allow
Principal:
Service: events.amazonaws.com
Action: sts:AssumeRole
Condition:
ArnEquals:
aws:SourceArn:
!Sub 'arn:aws:events:${AWS::Region}:${AWS::AccountId}:rule/aws-marketplace-event-rule-webhook-manual-${OrgId}'
Policies:
- PolicyName: event-bridge-iam-policy-invoke-api-destination
PolicyDocument:
Version: '2012-10-17'
Statement:
- Effect: Allow
Action: events:InvokeApiDestination
Resource: !GetAtt SugerMarketplaceApiDestination.Arn
SugerMarketplaceEventRule:
Type: AWS::Events::Rule
Properties:
Name: !Sub 'aws-marketplace-event-rule-webhook-manual-${OrgId}'
Description: Captures AWS Marketplace events and forwards to Suger
State: ENABLED
EventPattern:
source:
- aws.marketplacecatalog
- aws.agreement-marketplace
Tags:
- Key: SugerVersion
Value: '3'
Targets:
- Id: suger-api-destination
Arn: !GetAtt SugerMarketplaceApiDestination.Arn
RoleArn: !GetAtt SugerEventBridgeInvokeRole.Arn
Outputs:
RuleName:
Description: EventBridge Rule name. Enter this in the Suger console to register the setup.
Value: !Ref SugerMarketplaceEventRule
ConnectionArn:
Description: EventBridge Connection ARN
Value: !GetAtt SugerMarketplaceConnection.Arn
ApiDestinationArn:
Description: EventBridge API Destination ARN
Value: !GetAtt SugerMarketplaceApiDestination.Arn
EventRuleArn:
Description: EventBridge Rule ARN
Value: !GetAtt SugerMarketplaceEventRule.Arn
InvokeRoleArn:
Description: IAM Role ARN used by the rule to invoke the API Destination
Value: !GetAtt SugerEventBridgeInvokeRole.Arn
```
#### Register the rule in Fours
Once the stack is created, tell Fours which rule you made, so that it tracks your setup instead of trying to create its own:
1. On the [Integrations page](https://console.suger.io/settings?tab=integrations), open the **⋯** menu on your AWS Marketplace card and choose **Edit**.
2. At the bottom of the **Edit Integration** dialog, find **Register your EventBridge rule**. The section appears only while Fours has no EventBridge rule recorded for this integration.
3. Enter the name of your rule in `us-east-1` — the `RuleName` value on the stack's **Outputs** tab, `aws-marketplace-event-rule-webhook-manual-${OrgId}` if you deployed the template above unchanged — and click **Register existing setup**.
The registration is saved as soon as you click the button, and the section disappears. It records the setup; it does not prove that events flow — the [Verify](#verify) steps below do that.
A registered setup is yours, and Fours never changes it: its hourly setup leaves the rule, the rule's tags, the connection and its API key alone, and it never re-authorizes the connection. Fours only reads the setup — once right after you register it, then in the daily [delivery health check](#eventbridge-delivery-health). Those reads need the read-only actions `events:ListRules`, `events:ListConnections` and `events:ListApiDestinations` on the Fours Access IAM role, so keep them there.
Fours finds the connection and the API destination from the rule's name: whatever follows `aws-marketplace-event-rule-webhook` in the rule name must also follow `aws-marketplace-event-connection` and `aws-marketplace-event-api-destination` in theirs, as `-manual-${OrgId}` does in the template above. If you create the resources by hand instead, keep that pattern, or the health check cannot find them.
```d2
shape: sequence_diagram
you: "You"
aws: "Your AWS account\n(us-east-1)"
console: "Fours Console"
suger: "Fours"
you -> aws: "Deploy the EventBridge stack: connection,\nAPI destination, IAM role and rule"
you -> console: "Edit → Register your EventBridge rule\n→ Register existing setup"
console -> suger: "The rule name"
suger -> suger: "Record the setup as yours: never modified"
suger -> aws: "Read the rule, connection and API destination\n(read-only)"
events: "every AWS Marketplace event" {
aws -> suger: "Rule → API destination → Fours webhook,\nwith your auth ID as x-suger-api-key"
}
daily: "once a day" {
suger -> aws: "Read-only delivery health check"
}
```
#### Verify
1. Wait for the stack to reach `CREATE_COMPLETE`.
2. Trigger any AWS Marketplace action that emits an event — see the table below (for example, publish a private offer or have a buyer accept one).
3. On the [Integrations page](https://console.suger.io/settings?tab=integrations) of the Fours Console, scroll down to the **Auditing Events** table and confirm a new entry appears with **Source = `AWS_EVENT_BRIDGE`**. The **Action** column shows which AWS event arrived (e.g. `Offer Released`).

The AWS Marketplace activities that produce EventBridge events:
| AWS Marketplace activity | Auditing event action |
| ----------------------------------------------------------------- | ------------------------------------------------------------ |
| A private offer is published (released to the buyer) | `Offer Released` |
| A buyer accepts an offer — a purchase agreement is created | `Purchase Agreement Created - Manufacturer` / `- Proposer` |
| An existing agreement is amended (e.g. expansion, renewal) | `Purchase Agreement Amended - Manufacturer` / `- Proposer` |
| An agreement ends (expires or is cancelled) | `Purchase Agreement Ended - Manufacturer` / `- Proposer` |
| An agreement is approaching its end date | `Purchase Agreement Ending - Manufacturer` / `- Proposer` |
| An agreement is approaching an automatic renewal | `Purchase Agreement Renewal Upcoming - Manufacturer` / `- Proposer` |
| The terms of an automatic renewal are settled | `Purchase Agreement Renewal Terms Finalized - Manufacturer` / `- Proposer` |
| The license backing an agreement (entitlements) is updated | `License Updated - Manufacturer` |
| The license backing an agreement is deprovisioned | `License Deprovisioned - Manufacturer` |
The last three arrive only for agreements carrying [pre-authorized auto-renewal](/aws-marketplace/pre-authorized-auto-renewal/) terms, and they drive three entitlement email scopes you can route on the **Email notification** settings: `RENEW.ENTITLEMENT`, `AUTO_RENEW_OFF.ENTITLEMENT`, and `RENEW_SOON.ENTITLEMENT`.
**Offer Released** also brings in offers you did not create in Fours — one released from the AWS Marketplace Management Portal or the AWS Marketplace Catalog API, or a renewal offer AWS generates. Fours syncs such an offer as soon as the event arrives instead of waiting for the hourly sync. The offer's product must already be in Fours.
:::tip
Product change-set activity is not a reliable test: Fours deliberately filters out the `Change Set Succeeded` and `AWS API Call via CloudTrail` detail types, so they never appear in Auditing Events. Use an offer or agreement action from the table above instead.
:::
:::note The warning "Event Bridge Rule is not setup correctly." clears once you register the rule
Until you [register the rule](#register-the-rule-in-fours), the AWS Marketplace integration card in the Fours Console shows a warning icon with the message **"Event Bridge Rule is not setup correctly."**. The card shows it whenever Fours has no EventBridge rule recorded for the integration, and it does not affect event delivery.
 Registering the rule records it, and the warning goes away. Either way, the verification steps above (events arriving in the Fours Console) are the source of truth for whether delivery works.
:::
If events do not appear within a few minutes, check the EventBridge rule's **Monitoring** tab in the AWS Console for `FailedInvocations` and contact [Fours Support](mailto:support@suger.io) with the failure details.
#### Cleanup
When you remove the AWS Marketplace integration from Fours, also delete this stack from CloudFormation (in `us-east-1`) to clean up the EventBridge Connection, API Destination, Rule, and IAM Role it provisioned. See [Delete Integration](#delete-integration) for the standard cleanup steps.
## Enable Concurrent Agreements
Concurrent Agreements let your buyers hold multiple active agreements for the same AWS Marketplace product at the same time. That lets your sales team run expansion deals, multi-team procurement, and repeat purchases without waiting for a buyer's existing contract to renew or expire.
Starting **June 1, 2026**, AWS requires all new SaaS listings to support Concurrent Agreements. Fours handles the backend work for you — your responsibility is to confirm your EventBridge integration is active, submit the opt-in request to AWS, and complete a short validation test.
:::info
Concurrent Agreements also changes how usage metering works for the product — see [Usage Metering for AWS Concurrent Agreements](/metering/usage-metering/#usage-metering-for-aws-concurrent-agreements).
:::
:::important
If your product's **Product Type** is `Container`, Fours does not report its usage — with or without Concurrent
Agreements. Container and AMI products report their own usage from inside the running container or instance with AWS's
`MeterUsage` API, and Fours' metering API refuses usage for those listings with HTTP 400. See
[AMI & Container Products](/metering/usage-metering/#ami--container-products).
:::
### Does this apply to you?
| Your situation | What you need to do |
| ------------------------------------------------- | ------------------------------------------------------------------------------------------------------------ |
| New SaaS listing created after June 1, 2026 | Concurrent Agreements is already enabled. Confirm EventBridge is active in Fours, then you are done. |
| Existing SaaS listing created before June 1, 2026 | Concurrent Agreements is not enabled automatically. Complete all steps in this section. |
| Professional Services listing | Concurrent Agreements is enabled automatically by AWS. No action needed. |
| Product Type is `Container` | Fours does not meter Container listings, with or without Concurrent Agreements; the product reports its own usage with `MeterUsage`. See [AMI & Container Products](/metering/usage-metering/#ami--container-products). |
### Step 1: Confirm EventBridge is active
Concurrent Agreements require EventBridge to be enabled on your AWS integration in Fours. EventBridge is what lets Fours receive the `LicenseArn` parameter that uniquely identifies each concurrent agreement. Without it, the feature won't work.
1. Open the **Fours Console** and click **Settings**.
2. Click **Integrations**, then find the **AWS Marketplace** card.
3. Click **Details** on your AWS integration.

4. Make sure that `agreementEventBridgeEnrolled` = `true`.

If EventBridge is not enabled, complete the [Manual EventBridge Setup](#manual-eventbridge-setup) before continuing.
### Step 2: Submit the opt-in request to AWS
Existing SaaS listings require a support request to AWS before Concurrent Agreements can be enabled.
1. Open the [AWS Marketplace Contact Us form](https://aws.amazon.com/marketplace/management/contact-us/).
2. Fill in the form with the following selections:
- **Primary email address** — your preferred contact email
- **Which AWS Marketplace Catalog are you inquiring about** — Commercial Marketplace
- **What do you need help with** — Product Configuration / Integration
- **Select a subcategory** — Concurrent Agreements Support
3. Under **Provide more details about your request**, include:
- **Seller Account ID**
- **Fours Seller Name**
- **AWS Product ID(s)** for all public listings you want to migrate. To find these, open the **Fours Console**, go to **Products**, select your AWS Cloud Partner, and filter by **Status = Public**.
- **Number of active agreements** on each listing
- **Why you're opting in rather than creating a new listing** — AWS requires a brief explanation
4. Also request that AWS allow-list the Fours test buyer account for validation testing. Contact [Fours Support](mailto:support@suger.io) for the test buyer account ID.
5. Click **Message support** to send your request.
### Step 3: Create test private offers
AWS requires validation testing before completing the opt-in. For each pricing model your products use, create a test [private offer](/aws-marketplace/create-private-offer/) in Fours directed at the allow-listed Fours test buyer account.
Configure each test offer with:
| Field | Value |
| ------------- | -------------------------------- |
| Offer Name | Test Concurrent Agreement Offer |
| Buyer | Fours test buyer account ID |
| Contract Term | 1 month |
| Commit Amount | $1 |
| Terms | Standard AWS Marketplace Terms |
Create one offer per pricing model you use:
- **Contract** — fixed commitment
- **Usage** — usage-based only
- **Contract + Usage** — commitment with usage overage
### Step 4: Accept the test offer and report usage
1. Have your AWS admin accept each test private offer from the allow-listed buyer account.
2. If your product uses usage-based pricing, submit a small test usage record via the **Fours Console** to validate your metering pipeline:
| Field | Value |
| --------------- | ---------------------------- |
| Date | Current date |
| Usage Dimension | Your product's usage dimension |
| Quantity | 1 |
This generates approximately $0.01 in usage, which AWS uses to confirm your metering is working correctly.
### Step 5: AWS completes the migration
AWS reviews the test transactions to confirm that Concurrent Agreement events, entitlements, and usage reporting are all functioning correctly. Once validated, AWS completes the migration on their end and notifies you.
After migration, your team can immediately:
- Create multiple private offers for the same product and buyer simultaneously.
- Run expansion deals and mid-term upgrades without waiting for renewal dates.
- Support multi-team procurement with independent pricing and terms per agreement.
## EventBridge Delivery Health
EventBridge is how AWS Marketplace tells Fours that an offer was released, an agreement was created, or an entitlement changed. If that delivery path breaks, nothing errors out loudly — events simply stop arriving, and your offers and entitlements quietly go stale.
Fours closes that blind spot with a daily health check. Once a day it reads the delivery path straight out of your AWS account — the EventBridge rule, the connection, the API destination — and records the result on the AWS Marketplace integration.
### The four health states
| State | What it means | What Fours does |
| --- | --- | --- |
| `OK` | The full delivery path was verified healthy. | Nothing. |
| `INACTIVE` | The infrastructure is healthy, but no marketplace event has arrived in the last **30 days**. | Advisory only. Many low-activity accounts legitimately receive very few events, so this never interrupts you. |
| `DISCONNECTED` | A part of the delivery path is verified broken, so marketplace events are being dropped. | Fours Support is alerted; the hourly sync re-authorizes a deauthorized connection automatically. |
| `N_A` | EventBridge was never set up for this integration. | Nothing. |
```d2
direction: down
check: "Daily health check\nreads the delivery path from your AWS account"
setup: "EventBridge set up\nfor this integration?" { shape: diamond }
path: "Rule, connection and\nAPI destination all healthy?" { shape: diamond }
fresh: "An event received\nin the last 30 days?" { shape: diamond }
na: "N_A"
disconnected: "DISCONNECTED\nevents are being dropped"
inactive: "INACTIVE\nadvisory only"
ok: "OK"
check -> setup
setup -> na: "no"
setup -> path: "yes"
path -> disconnected: "no"
path -> fresh: "yes"
fresh -> inactive: "no"
fresh -> ok: "yes"
```
### Why the path was reported DISCONNECTED
The check records a specific reason, which Fours Support uses to point you at the fix:
| Reason | What broke |
| --- | --- |
| `NOT_CONFIGURED` | The integration exists but EventBridge was never set up. |
| `ACCESS_DENIED` | Fours cannot assume the integration IAM role, or is denied the EventBridge read APIs — usually a deleted CloudFormation stack. |
| `RULE_MISSING` | The EventBridge rule no longer exists. |
| `RULE_DISABLED` | The rule exists but is disabled. |
| `CONNECTION_MISSING` | The API-key connection no longer exists. |
| `CONNECTION_DEAUTHORIZED` | AWS deauthorized the API-key connection, so events are dropped. Fours re-authorizes the connection automatically on its next hourly sync. |
| `API_DESTINATION_MISSING` | The API destination no longer exists. |
| `API_DESTINATION_INACTIVE` | The API destination exists but is not active. |
| `NO_RECENT_EVENTS` | The infrastructure is healthy, but no event has arrived recently. This is the `INACTIVE` reason. |
:::tip
If you set EventBridge up manually rather than through the Fours CloudFormation stack, the health check sees your setup only once you [register the rule](#register-the-rule-in-fours). Until then it reports `N_A`, because Fours has no rule recorded for the integration. After you register it, the check reads your rule, connection and API destination by name without changing them — and if the Fours IAM role is not allowed to read EventBridge resources in your account, it reports `ACCESS_DENIED`. Either way, the [Verify](#verify) steps — real events landing in the **Auditing Events** table — are the source of truth.
Fours re-authorizes a deauthorized connection only on a setup it created. If the connection of a setup you registered is deauthorized, re-authorize it yourself: update the connection in the EventBridge console with the same API key, your organization's auth ID.
:::
## Marketplace Commerce Analytics Service (MCAS)
The Commerce Analytics Service accesses the Amazon S3 bucket and Amazon SNS topic after you configure the service with the ARN for the topic and name of the bucket. To enable MCAS, please follow the steps below. For more details, see the [documentation](https://docs.aws.amazon.com/marketplace/latest/userguide/commerce-analytics-service.html#technical-implementation-guide).
1. Log in to the [AWS Marketplace Management Portal](https://aws.amazon.com/marketplace/management/) with the AWS account you use to manage your AWS Marketplace products.
2. Ensure you have the [necessary IAM permissions](https://docs.aws.amazon.com/marketplace/latest/userguide/commerce-analytics-service.html#technical-implementation-guide) to enroll in the AWS Marketplace Commerce Analytics Service.
3. Navigate to the [Commerce Analytics Service enrollment page](https://aws.amazon.com/marketplace/management/cas/enroll).
- Select `Use an existing IAM role`
- Select IAM role as the default `MarketplaceCommerceAnalyticsRole`
- Set S3 bucket name `suger-mcas-s3-bucket-{aws-account-id}`
- Set SNS topic ARN `arn:aws:sns:us-east-1:{aws-account-id}:suger-mcas-sns-topic`
- Click the `Enroll` button
:::warning
- If you have enrolled the MCAS before, please contact us to get custom configuration. We will update the IAM policy of the IAM role `MarketplaceCommerceAnalyticsRole` to support the right S3 bucket & SNS topic.
:::
4. On the AWS Marketplace Management Portal, record the Role Name ARN in the success message.
:::note
If AWS reports that your account is not set up for the Commerce Analytics Service — it is not registered as a Marketplace seller, or has no MCAS subscription — Fours turns on **MCAS Sync Disabled** for the integration and stops requesting MCAS data, because retrying cannot succeed. Once you have completed the enrollment above, edit the integration and turn **MCAS Sync Disabled** off so the sync resumes.
:::
## Marketplace Data Feeds Service (MDFS)
To get the full structured, up-to-date product billing and customer information from AWS Marketplace, it is highly recommended to set up the [Data Feeds Service](https://docs.aws.amazon.com/marketplace/latest/userguide/data-feed-service.html). Follow the below steps:
:::warning
- If you have set up the field `MdfsS3BucketName` with `suger-mdfs-s3-bucket-{your-aws-account-id}` in the previous cloud formation stack of AWS Marketplace integration, please skip the following **step 1** & **step 2** since the MDFS S3 bucket and KMS have been created.
:::
1. Go to the [Data Feed Configuration page](https://aws.amazon.com/marketplace/management/reports/data-feed-configuration).
2. Click `Configure with Cloud Formation`, a new page with stack template will be opened. Type in the `Stack name` with `mp-data-feed` (don't change this name since it is recognized by Fours service), and the `S3BucketName` with an unique S3 name `suger-mdfs-s3-bucket-{aws-account-id}`. Then click button `Create stack`.
:::warning
- The `stack name` must be `mp-data-feed`. Otherwise, Fours service won't recognize.
- The `S3BucketName` must be `suger-mdfs-s3-bucket-{aws-account-id}`. Otherwise, suger service won't have permissions to access.
- The stack must be running in the AWS region `us-east-1`, not other regions.
:::
>
 3. Once the upper Cloud Formation stack is 'CREATE_COMPLETE', find the `S3 Bucket ARN` (for example: `arn:aws:s3:::suger-mdfs-s3-bucket-{aws-account-id}`) and the `KMS Key ARN` (for example: arn:aws:kms:us-west-2:awsAccountId:key/keyId), and input them to the [Data Feed Configuration page](https://aws.amazon.com/marketplace/management/reports/data-feed-configuration). Click buttion `Submit`.
4. Fours service take all the rest of setup and cron data sync pipeline.
### FAQ
### My Security team asked about the need for a KMS access policy. How does Fours use KMS in our account?
The KMS access is for MDFS integration, which syncs revenue data and buyer information (company name, address, and email domain).
AWS requires all S3 buckets for marketplace revenue and buyer reports to be encrypted by a KMS key. This KMS key is created via the cloud formation template provided by AWS.
[More details can be found here](/aws-marketplace/integration/#marketplace-data-feeds-service-mdfs).
Fours doesn’t require general access to your KMS resources; it is only limited to the one related to the MDFS integration.
## Set up Tax & Banking Info
AWS marketplace requires the seller/ISV to provide valid Tax & Banking Info before selling paid or BYOL (bring your own license) products. Please visit the [setting page](https://aws.amazon.com/marketplace/management/seller-settings/account) of your AWS marketplace management portal, and submit the tax information & banking information (to collect revenue from marketplace sales).
### Tax Information
The following fields for tax information are required:
1. **Federal tax classification**. Most companies are `C Corporation`, and the others may be `S Corporation`, `Partnership` or `Limited liability company`.
2. **Business Name** and **Business Address**
3. **EIN** (Federal Employer Identification Number)
>
 ### Banking Information
The following fields for banking information are required:
1. **Bank account address**, the address on your company bank account.
2. **Bank account holder name**, in most cases, it is your company legal name.
3. **Routing Number**
4. **Account Number**
>
 ## AWS Payment Flow
When a customer purchases your product on AWS Marketplace, the transaction follows AWS's billing and payment structure:

1. The customer subscribes to or purchases your product.
2. AWS generates an invoice and adds it to the customer's consolidated AWS billing.
3. The customer pays AWS according to their payment terms (for example, net 30, 45, or 60 days).
4. Once AWS receives the payment, it disburses to you based on your selected disbursement cycle (daily or monthly).
:::info
- AWS disburses payments to sellers **only after** receiving payment from the customer. For example, if a customer on net 60 terms buys your product today, payment is due to AWS in 60 days, and only after AWS receives it will you be paid.
:::
### Disbursement cycles
Choose your disbursement cycle in the [AWS Marketplace Management Portal](https://aws.amazon.com/marketplace/management/seller-settings/account) under **Payment Information**:
- **Daily** — AWS pays as soon as payment becomes available.
- **Monthly** — AWS pays on a fixed day (1–28) of each month.
### Currency and exchange rates
Offers are created in **USD**, customers are billed in their **local currency**, and AWS uses **Bloomberg exchange rates** to convert. See [Multi Currency](/aws-marketplace/create-private-offer/#multi-currency) for creating offers in non-USD currencies.
### Track expected payment in Fours
To check when AWS is expected to receive payment from the buyer:
1. Go to the **Entitlement** menu.
2. Click the entitlement in question.
3. Open the **Revenue** tab.
4. Scroll to the **Due Date** column in the revenue table — this shows the estimated date the buyer will pay AWS.
:::tip
- The **Due Date** is not the date the money is disbursed to your account. AWS processes disbursement only **after** this payment is received.
:::
### Common payment issues
Payments can be delayed by incorrect account permissions, declined credit cards, or customer billing setup issues. Make sure your customers have a valid payment method and a correctly configured AWS account. If payment is delayed beyond the expected due date, open a support case on the [AWS Marketplace Management Portal](https://aws.amazon.com/marketplace/management/contact-us/).
## FAQ
### Who do I receive the payment from?
Payment will always be deposited into your registered bank account. To check your registered bank account, visit the [Settings section](https://aws.amazon.com/marketplace/management/seller-settings/account) on AMMP > Payment Information.
### How much listing/transaction fee does AWS take?
Listing fees depend on the type of listing, TCV of the offer, and type of offer. The document below is an official document by AWS that covers the fee structure for all scenarios.
https://docs.aws.amazon.com/marketplace/latest/userguide/listing-fees.html
### When is the customer billed?
AWS bills the customer based on three ways:
1. Date of subscription acceptance (upfront billing)
2. Custom payment schedule (private offers built by flexible payment scheduler)
3. Metered usage on the second and third day of the month for the prior month’s usage
### When will I receive money from AWS?
Every customer has agreed to net payment terms with AWS — commonly net 30, 45 or 60, and net 0 for credit cards. Once a customer receives the bill, they must pay the amount within the agreed terms.
You can also override that per offer: a private offer can carry its own **Buyer net payment term** of Net 15, 30, 45, 60, 90, or 120 days. See [Buyer net payment term](/aws-marketplace/create-private-offer/#buyer-net-payment-term). A longer term delays when AWS collects, and therefore when AWS disburses to you.
Every seller has a disbursement cycle, which can be set up under settings. There are two cycles: daily and monthly. You can receive the money as soon as the AWS receives it or on a specific date every month.
To check your registered bank account, visit the [Settings section](https://aws.amazon.com/marketplace/management/seller-settings/account) on AMMP > Payment Information > Update Banking Information > Disbursement Preference.
### Do I need to charge and remit taxes separately?
This depends on the buyer's country. In countries such as the USA, where the marketplace is responsible for collecting and remitting taxes, this function will be handled by AWS itself. In other countries, such as France, the Seller must collect the tax manually.
AWS's video [AWS Marketplace Tax Rules](https://youtu.be/qaBDxNiZkho) explains how AWS assesses tax and how it affects invoicing.
AWS's [Tax Help for Sellers](https://aws.amazon.com/tax-help/marketplace-sellers/) covers taxes on different product types, the countries supported, and the process.
### What should we do if there is a delay in receiving payments from AWS?
You can open a ticket with AWS through the [AWS Marketplace contact form](https://aws.amazon.com/marketplace/management/contact-us/).
### How to process refunds?
You can process a full or partial refund to the buyer by submitting AWS's [refund request form](https://aws.amazon.com/marketplace/management/support/refund-request).
You can request a refund even when the buyer has not yet paid the invoice. In the additional comments section, mention that the charges should be waived if they are unpaid.
### Can I invoice a customer in their currency?
You will create private offers in Dollars ($) as a seller. AWS will, in turn, check the buyer's currency based on the account ID and the payment settings and then bill them in their currency.
AWS uses exchange rates published by Bloomberg every day. See AWS's [list of supported currencies](https://docs.aws.amazon.com/marketplace/latest/buyerguide/buyer-paying-for-products.html#supported-currencies) for the current set.
### We have an offer that was accepted, but the payment transaction failed. Is there a way to reprocess the transaction?
If a private offer acceptance fails due to an issue with the customer's payment method/account, the customer can try accepting the same private offer again after it is fixed. This time, it should go through. The offer they initially accepted didn't generate any entitlement because it wasn't processed. They can use the same offer link to accept it again, and it should work this time.
### We have an offer that the customer has tried to accept three times, and we get an acceptance email and then immediately get a cancellation email. Is this a typical payment issue? Is there something that you'd advise us to tell the customers to solve this?
There are three main reasons why an offer acceptance might fail:
1. The person trying to accept the offer doesn't have the proper permission to complete that transaction.
2. Their credit card operator declined the transaction, or they have not correctly set up their account for payment.
3. AWS can reject them from transacting if they have not paid their latest billing.
Usually, it's a problem with the customer's credit card or with their payment account in general. You can contact the customer to have them help you verify the transaction.
We recommend asking in the discovery if they are on an Invoice or Credit Card with AWS. If they are on a Credit Card, tell them they need to make sure that their Bank knows this transaction is about to be processed so that it does not get rejected, as often Credit Card companies will reject due to the size of the transaction as possible fraud.